Table of Contents
- Pre-Deployment Engineering: Site Surveys and Door Schedules
- OSDP v2 vs. Wiegand Security: Why Encryption Matters
- Enterprise Access Control Network Segmentation Best Practices
- Lock Hardware Selection: Strikes, Maglocks, and Code Compliance
- NFPA 101 Egress Compliance for Access Control
- Cloud vs. On-Premises Architecture for Multi-Site Enterprises
- Access Control System Commissioning Checklist
- Frequently Asked Questions
Last Updated: September 18, 2026
Pre-Deployment Engineering: Site Surveys and Door Schedules
Enterprise access control system installation begins long before anyone mounts a reader. It starts with a site survey and a door schedule, and that documentation decides whether the deployment scales or collapses under its own exceptions.
A door schedule is the master document of the project. It lists every opening, its hardware type, its locking method, its power source, and its egress classification. Skip it and you will discover the gaps during commissioning, when changes cost the most.
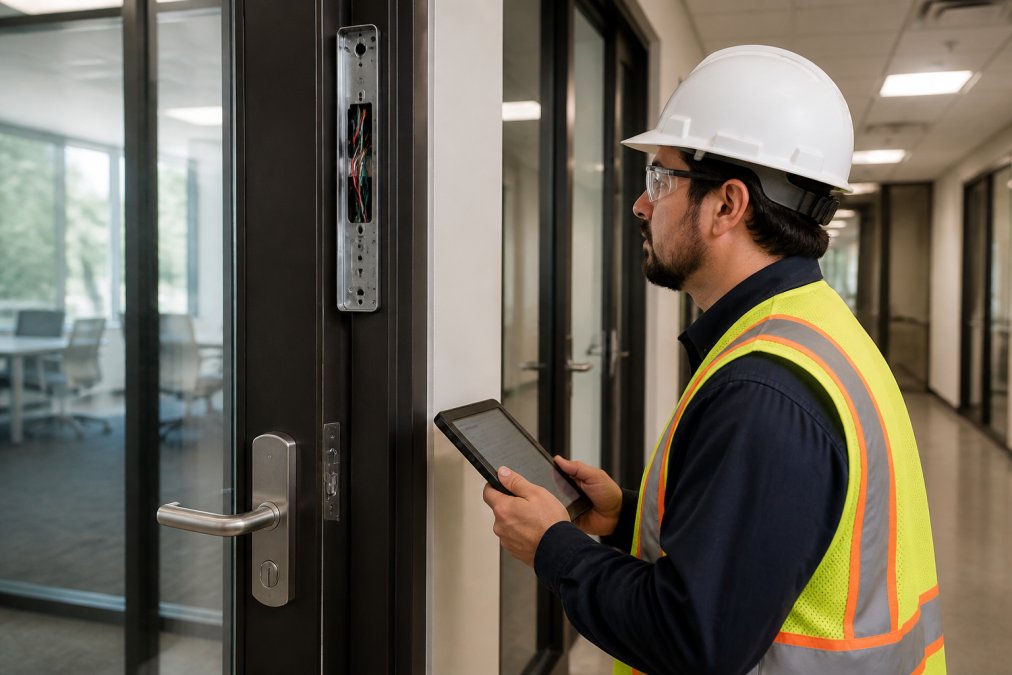
At Systems Integrations, we treat the survey as an engineering exercise, not a sales walkthrough. Our teams measure frame dimensions, verify existing power runs, and map every credential reader to a controller port before a single cable is pulled.
Power Infrastructure and Centralized Supplies
Centralized power is the backbone of any enterprise access control system installation. Distributing individual power supplies at each door creates maintenance headaches and battery failures nobody can track.
A centralized supply with battery backup keeps every controller and lock energized through an outage. In practice, this means one monitored cabinet per floor or riser instead of a dozen unmanaged bricks behind ceiling tiles.
Label every power run at both ends with the door number, not the room name. Room names change; door numbers on the schedule do not.
OSDP v2 vs. Wiegand Security: Why Encryption Matters
Legacy Wiegand is unencrypted by design. Anyone who can reach the reader-to-controller wiring can tap it, capture credential data, and replay it later. OSDP v2 with Secure Channel Protocol encrypts that traffic and detects tampering in real time.
The difference is not academic. A Wiegand run in a shared riser or an accessible junction box is a credential-cloning opportunity. OSDP v2 authenticates the reader to the controller and the controller to the reader, so an injected device cannot impersonate either end.
| Attribute | Legacy Wiegand | Enterprise OSDP v2 |
|---|---|---|
| Encryption | None | AES-128 Secure Channel |
| Wire runs | Parallel, unmonitored | Supervised, tamper-detecting |
| Credential protection | Plaintext | Encrypted |
| Device authentication | None | Mutual |
| Firmware updates | Manual | Remote |
| Multi-site scaling | Limited | Native |
If your existing readers are Wiegand, plan the migration before you add doors. Retrofitting encryption later means re-pulling cable and re-terminating controllers.
Enterprise Access Control Network Segmentation Best Practices
Network segmentation is the control that separates a hardened access control system from an IoT liability. Every door controller is a network device, and every network device is an attack surface.
The rule is simple: no controller touches the corporate LAN, and no controller has a public IP address. Access control traffic stays in its own VLAN, reachable only through a firewall rule that permits the management server to poll it.
VLAN Isolation and 802.1X NAC
VLAN isolation keeps badge data and door events off the business network. 802.1X network access control goes further: it authenticates the controller itself before granting it a port.
With 802.1X, a stolen controller cannot simply be plugged into a switch and trusted. The switch demands credentials, the certificate check fails, and the port stays closed. For multi-site enterprises, this is the difference between a contained incident and a lateral breach.
Controllers left on the corporate VLAN with default credentials are the most common finding in post-installation audits. One compromised controller can expose every door schedule on the network.
Lock Hardware Selection: Strikes, Maglocks, and Code Compliance
Lock hardware selection drives both security and code compliance, and the wrong choice fails inspection. Electric strikes, electrified mortise locks, and magnetic locks each solve a different problem, and each carries its own code triggers, power requirements, and failure modes.
Electric strikes release the latch and let the door swing free. They are the least invasive retrofit because the existing frame accepts a strike cut, but they depend on the door’s mechanical lock body remaining functional. A strike on a door with a worn latch or misaligned frame will fail intermittently, and intermittent failures are the hardest to diagnose during commissioning. Strikes are typically fail-secure: power releases the latch, and a power loss leaves the door locked. That is acceptable on a perimeter door but not on a required egress path unless paired with a fail-safe release mechanism.
Electrified mortise locks replace the entire locking body, giving you tighter control over the latch and a cleaner install on new construction. They cost more in labor and hardware, but they eliminate the frame-fit variables that plague strikes. On a high-traffic egress door, the mortise lock is often the more reliable long-term choice because the locking mechanism and the electrification are engineered together rather than adapted.
Magnetic locks hold the door with electromagnet force. They are strong and simple, but they fail secure by default, meaning they stay locked when power drops.
| Lock Type | Fail Mode | Best Application | Code Trigger |
|---|---|---|---|
| Electric strike | Fail-secure (typical) | Retrofit perimeter and interior doors | Egress release required on egress doors |
| Electrified mortise | Configurable | New construction, high-traffic egress | Egress release required on egress doors |
| Magnetic lock | Fail-secure | Non-egress, high-security openings | REX, DPS, and release required on egress |
Match the lock to the egress classification first, then to the security requirement. A maglock on an egress door without proper release hardware is a code violation, not a design choice.
Every electronically locked egress door must release on the egress side with a single motion and must release automatically when the fire alarm activates. Verify the fire alarm control panel (FACP) interface drops power to the locks on alarm before you finalize the door schedule.
NFPA 101 Egress Compliance for Access Control
NFPA 101 egress compliance is non-negotiable: no access control system may prevent free egress. Every electronically locked door must release on the egress side with a single motion, and it must release automatically when the fire alarm activates.
Cloud vs. On-Premises Architecture for Multi-Site Enterprises
Cloud-managed access control has become the default for distributed enterprises, and the reason is operational, not fashionable. A cloud platform pushes firmware, syncs credential changes across sites, and gives you one pane of glass for every door. On-premises servers still make sense in specific cases: air-gapped facilities, strict data residency requirements, or sites with unreliable WAN links. The trade-off is that you own the patching, the backups, and the failover.
Enterprise Integrations: Video Verification and Visitor Management
A cloud-managed access control platform is only as useful as the systems it talks to. Two integrations matter most for enterprise deployments.
Post-Installation Audit and Compliance Reporting
Enterprise clients need documentation for insurance and regulatory audits, and this is where cloud platforms separate from on-premises servers. A cloud platform can generate access logs, encryption status reports, and firmware version reports on demand. An on-premises server can do the same, but only if someone maintains the reporting scripts and the backup schedule. In practice, on-premises reporting drifts because it depends on a person, not a platform.
For multi-site portfolios, standardize the cloud platform across every location. A single platform means a single audit report, a single firmware schedule, and a single point of contact when something fails.
Access Control System Commissioning Checklist
An access control system commissioning checklist converts installation into acceptance. Work through it in order and you catch failures while they are still cheap to fix.
Enterprise Installation & Commissioning Checklist
Pre-Wire
- Door schedule matches installed hardware at every opening
- Cable runs labeled at both ends with door numbers
- Power runs verified for voltage drop and gauge
Lock Prep
- Lock type matches egress classification
- Request-to-exit sensors and door position switches installed
- Fire alarm release interface wired and tested
Controller Wiring
- OSDP v2 readers terminated and encrypted
- Controllers on isolated VLAN with no public IP
- 802.1X authentication confirmed at the switch port
Testing & Acceptance
- Every credential tested at every reader
- Door forced open and door held open events verified in the video system
- Fail-safe and fail-secure behavior confirmed under power loss
- Audit trail populated and reviewed
Testing, Acceptance, and Post-Installation Audit
Commissioning ends with acceptance testing, but the work continues with a post-installation audit. That audit confirms firmware is current, credentials are still valid, and no door has drifted out of compliance since handover.
Frequently Asked Questions
What are the NFPA 101 requirements for electronic access control egress?
NFPA 101 requires that egress doors unlock immediately upon occupant approach in the direction of travel without prior knowledge or effort. Access control systems must fail safe, releasing locks on power loss or fire alarm activation. Delayed egress is permitted only on select occupancy types with specific signage, and all doors must tie into the fire alarm control panel for automatic release during emergencies.
Why is OSDP v2 considered the standard for secure enterprise access control?
OSDP v2 uses AES-128 encryption over the reader-to-controller channel, preventing wire tapping and replay attacks that plague legacy Wiegand. It supports bidirectional communication for real-time tamper detection and firmware updates. For enterprises with compliance requirements, OSDP v2 provides the audit trail and encryption protocols needed to meet cybersecurity frameworks.
How does network segmentation protect physical security systems from cyber threats?
Segmenting access control onto isolated VLANs prevents lateral movement if a corporate network is compromised. Best practices include denying public IP exposure, enforcing 802.1X network access control, and using firewalls between the security VLAN and IT infrastructure. This architecture ensures door controllers and cameras remain operational and uncompromised even during broader network incidents.
How do enterprise access control systems integrate with NDAA-compliant video surveillance?
Integration links door events like Door Forced Open or Door Held Open to video verification, automatically pulling up live or recorded footage when an alarm triggers. This requires API integration between the access control platform and VMS. For NDAA compliance, verify all cameras and recorders originate from approved manufacturers, avoiding banned entities in the supply chain.